
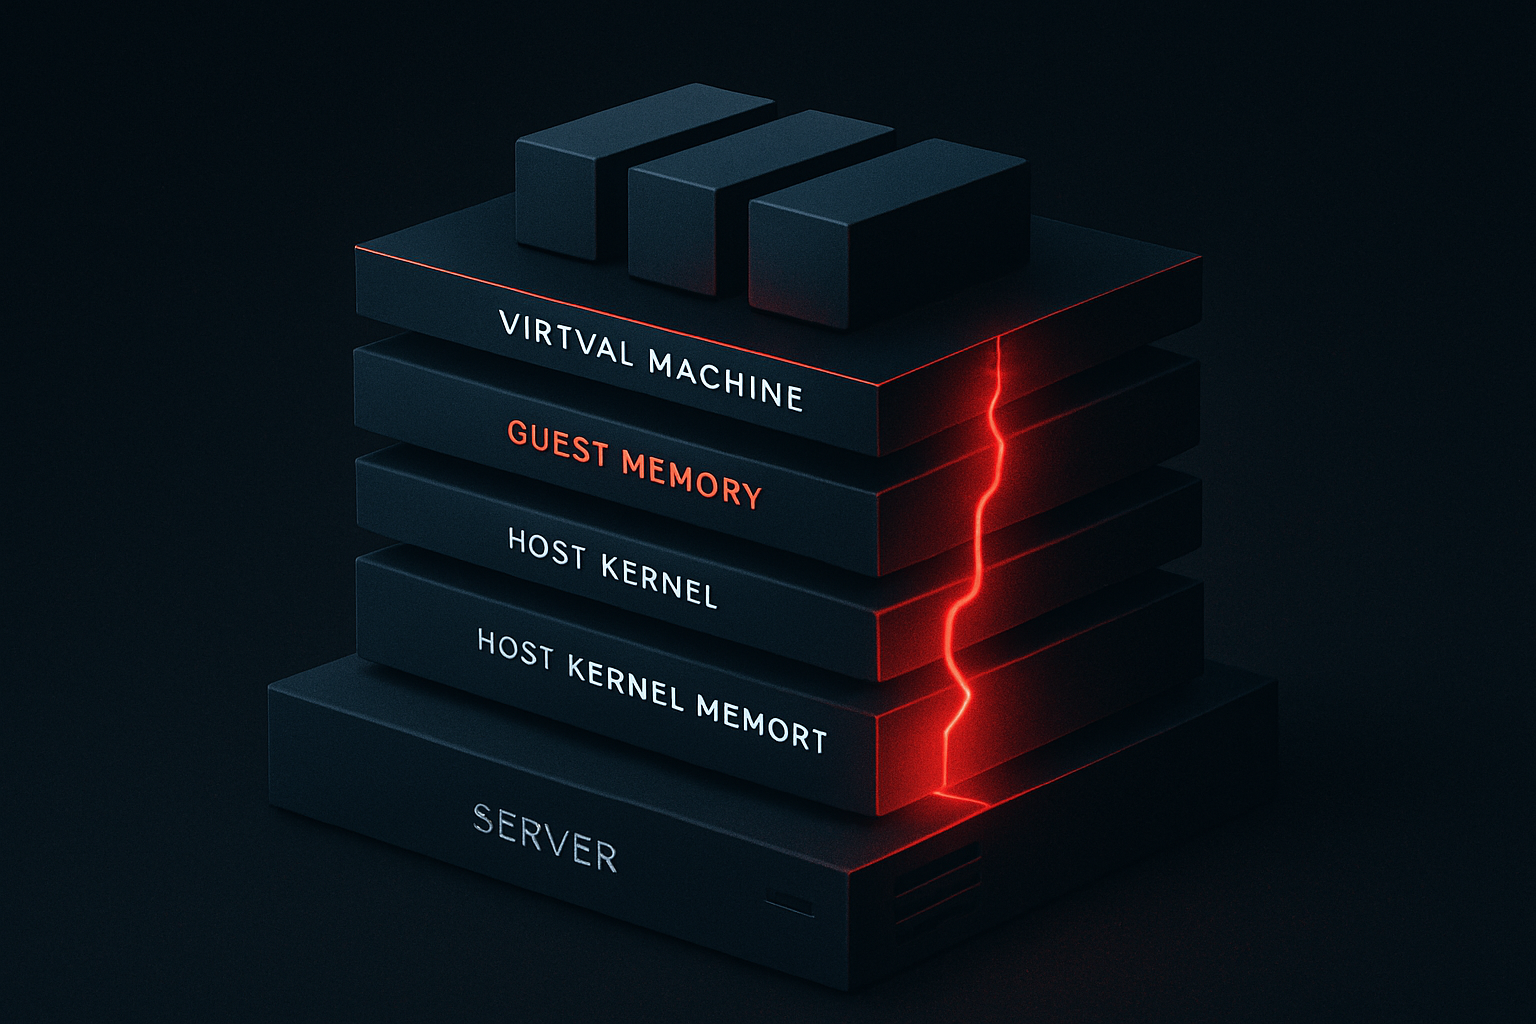
A critical vulnerability in the Linux kernel's networking stack has emerged that undermines a fundamental assumption in virtualised hosting: that guest operating systems cannot read or modify the memory of their host. The flaw, tracked as CVE-2026-99999 and dubbed PwnEscape, demonstrates a clean path from within a sandboxed virtual machine to host kernel memory, with implications that ripple across the entire shared hosting ecosystem.
The Scope of the Problem
The vulnerability resides in the Linux kernel's networking code—not in hypervisor configuration, container runtime, or any particular cloud provider's setup. This is significant. Unlike misconfigurations that can be patched at the deployment layer, a kernel-level flaw affects all systems running vulnerable versions, regardless of how carefully they've been hardened. A researcher successfully demonstrated the attack against live sandboxes operated by Vercel, confirming the vulnerability is exploitable in production environments running standard kernel versions.
For infrastructure providers, the attack surface extends across any multi-tenant deployment where VMs or containers share host hardware: traditional dedicated server virtualisation, VPS platforms, Kubernetes clusters, and serverless compute environments. Even isolated guest workloads can potentially exfiltrate sensitive data from the host kernel or neighbouring tenants if they share memory pools.
Why Networking Code Is the Weak Point
The kernel's networking subsystem occupies a unique attack surface. It handles data ingress from untrusted network interfaces, processes packets in contexts where memory protections can be bypassed, and often operates with elevated privileges. Vulnerabilities in this area are particularly dangerous because they sit at the boundary between user-controlled input and kernel internals. A guest VM can generate specially crafted packets that trigger memory disclosure in the host kernel—without requiring code execution on the host itself.
This attack vector is difficult to mitigate through conventional network segmentation. The flaw doesn't require accessing a service or exploiting a userspace daemon; it works against the kernel's core packet processing logic, which every connected system must run.
Immediate and Longer-Term Remediation
Hosting providers have two parallel tracks. In the short term, the affected kernel versions require patching. Providers should prioritise this across production hypervisors, taking advantage of live kernel patching where available to avoid extended downtime. Testing must verify that patches don't introduce regressions in network performance—a common risk when kernel networking code changes.
Longer term, this vulnerability underscores the value of additional isolation layers. Providers already using nested virtualisation, seccomp, or AppArmor profiles gain some defence-in-depth; those relying solely on standard KVM or Xen isolation are more exposed. For dedicated server operators, this is also a reminder to audit which guests are running untrusted workloads on shared systems, and to consider stronger isolation if revenue and use-case mix permit.
The original disclosure details the technical mechanics of the exploit, but the practical lesson is clear: kernel vulnerabilities in core subsystems like networking can nullify an entire layer of virtualisation security.
Organisational Response
Teams should begin with inventory: which kernel versions are running on production hypervisors, and what upgrade windows are realistic. Test patches in staging first, paying particular attention to network throughput and latency under load. Communicate with customers transparently about patching plans, and consider security advisories for guests running sensitive workloads on shared infrastructure.
For those operating private or dedicated hosting environments, this is a prompt to validate your hypervisor patching schedule and to confirm whether your support contracts include out-of-band security updates. The time between CVE publication and mass exploitation is often measured in weeks.
PwnEscape is a reminder that virtualisation security rests on many layers, and that kernel-level flaws remain a real threat even when everything else is configured correctly. Patching is not optional; it's foundational.


